Cybersecurity researchers are warning of two cybercrime groups conducting rapid, high-impact attacks within SaaS environments while leaving minimal traces. Cordial Spider, also known as BlackFile, CL-CRI-1116, O-UNC-045, and UNC6671, and Snarky Spider, also known as O-UNC-025 and UNC6661, have been linked to high-speed data theft operations.
Cybercrime Groups Using Vishing and SSO Abuse in Rapid SaaS Extortion Attacks
Cybersecurity researchers are warning of two cybercrime groups conducting rapid, high-impact attacks that operate within SaaS environments while leaving minimal traces. Cordial Spider (also known as BlackFile, CL-CRI-1116, O-UNC-045, and UNC6671) and Snarky Spider (also known as O-UNC-025 and UNC6661) have been linked to high-speed data theft operations.
China-Linked Hackers Target Asian Governments, NATO State, Journalists, and Activists
Cybersecurity researchers have disclosed details of a new espionage campaign linked to China targeting government and defense sectors across South, East, and Southeast Asia, as well as one European NATO member state. Trend Micro has attributed the activity to a threat group it tracks under the temporary designation SHADOW-EARTH-053.
Top Five Sales Challenges Costing MSPs Cybersecurity Revenue
The managed security services market is projected to grow from $38.31 billion in 2025 to $69.16 billion by 2030, with cybersecurity being the fastest-growing sector. Despite this market opportunity, many MSPs fail to capture available revenue because their go-to-market strategy does not effectively align technical expertise with business needs. This execution gap is where most deals stall, as MSPs often focus on technical capabilities rather than addressing client business objectives.
Two Cybersecurity Professionals Get 4-Year Sentences in BlackCat Ransomware Attacks
The U.S. Department of Justice announced the sentencing of two cybersecurity professionals to four years in prison each for their involvement in BlackCat ransomware attacks. Ryan Goldberg, 40, from Georgia, and Kevin Martin, 36, from Texas, were convicted of deploying the ransomware against multiple victims across the United States between April and December 2023.
Poisoned Ruby Gems and Go Modules Exploit CI Pipelines for Credential Theft
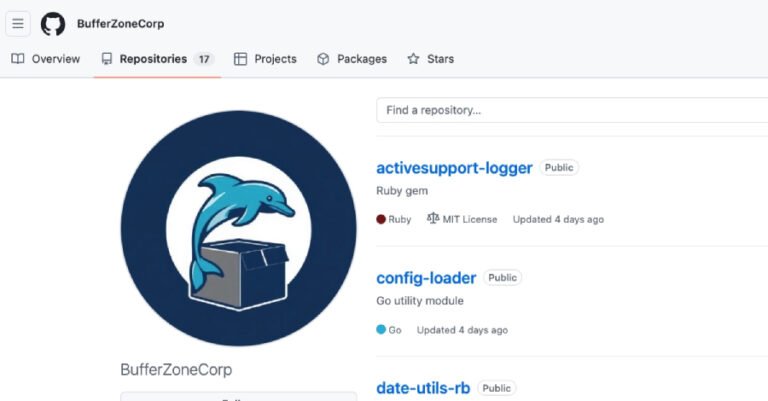
A software supply chain attack campaign has been identified using sleeper packages to distribute malicious payloads capable of stealing credentials, tampering with GitHub Actions, and establishing SSH persistence. The activity has been linked to the GitHub account BufferZoneCorp, which published repositories containing malicious Ruby gems and Go modules.
PyTorch Lightning and Intercom-client Hit in Supply Chain Attacks to Steal Credentials
Two Python packages, PyTorch Lightning and Intercom-client, were compromised in separate supply chain attacks designed to steal credentials. According to Aikido Security, OX Security, Socket, and StepSecurity, malicious versions 2.6.2 and 2.6.3 of PyTorch Lightning were published on April 30, 2026.
ThreatsDay Bulletin: SMS Blaster Busts, OpenEMR Flaws, 600K Roblox Hacks and 25 More Stories
This week brings multiple cybersecurity threats. Attackers are using fake cell towers to send fraudulent text messages, while developers are unknowingly downloading malicious tools that access private files during installation. Additionally, millions of servers remain online without password protection, creating significant security vulnerabilities.
Space Force’s 15-year vision calls for more personnel, simulators and survivability
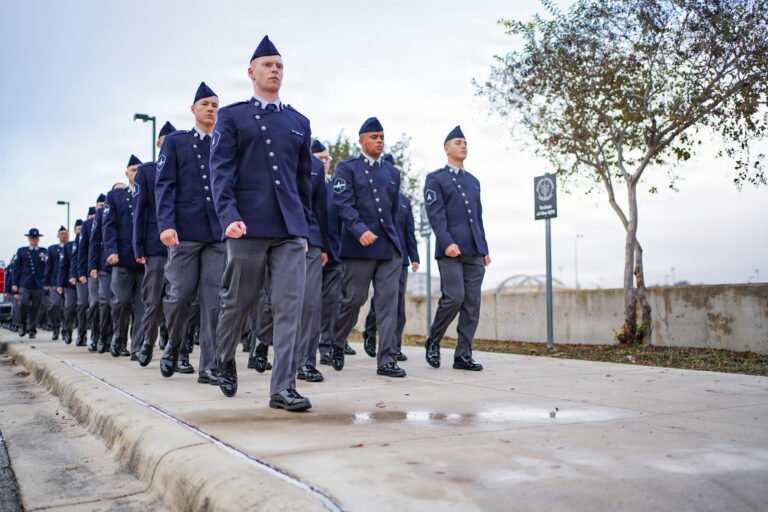
The Space Force has released a vision document outlining its 15-year strategic plan, which addresses the evolving landscape of space warfare and the service’s preparedness strategies.
Starlink outage hit drone tests, exposing Pentagon’s growing reliance on SpaceX
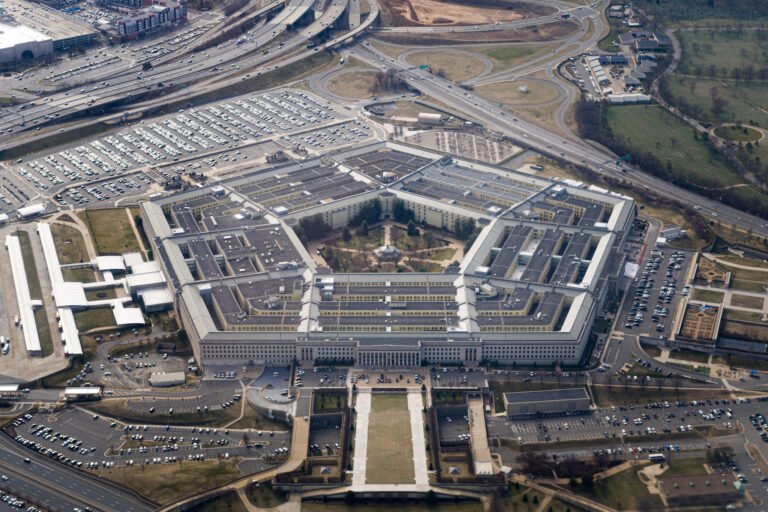
A global outage affecting Elon Musk’s satellite network in August left U.S. Navy unmanned surface vessels unable to operate off the coast of California, halting their operations.